The leading PreVeil alternative for CMMC
Choose the platform that covers CMMC compliance end-to-end.
Secureframe Defense automates the work of implementing and maintaining NIST 800-171 compliance and CMMC. Get guided scoping, automated Microsoft GCC High or Google Workspace configuration, Windows 11 virtual desktops and Federal MDM for endpoint scope control, and documentation generated from your live environment. The Secureframe Platform is FedRAMP 20x Class C (Moderate) certified, and Secureframe is CMMC Level 2 certified and a Registered Provider Organization in the Cyber AB Marketplace.
PreVeil is an end-to-end encrypted email and file-sharing overlay (PreVeil Email and Drive) that protects CUI within your existing environment, for contractors with narrow CUI exposure. It works alongside any client, including commercial Microsoft 365 and Google Workspace, so you still need and pay for that underlying subscription. Calendar, chat, meetings, and document editing stay on the tenant you already run. In mid-2026 PreVeil added a managed virtual desktop offering on Amazon WorkSpaces in AWS GovCloud.
How Secureframe Defense and PreVeil compare for CMMC
| What to compare | Secureframe Defense | PreVeil |
|---|---|---|
| CMMC Level 2 certified | Yes | Yes |
| Registered RPO in the Cyber AB Marketplace | Yes | No |
| NIST 800-171 controls addressed | All 110 | 102 of 110 |
| Automated CMMC-compliant enclave provisioning | Yes | No |
| Microsoft GCC High licensing, provisioning, and drift monitoring | Yes | No |
| Google Workspace for CMMC | Yes | No |
| Windows 11 virtual desktops with dedicated, pooled, and GPU options | Yes | No |
| Federal MDM for laptops and endpoints | Yes | No |
| Continuous control monitoring | Yes | No |
| 24/7 security operations (SOC) services | Yes | No |
| vCISO services | Yes | No |
| Automated evidence collection from cloud and endpoints | Yes | No |
| SSP generated from your live environment | Yes | No |
| Real-time SPRS scoring | Yes | No |
| FedRAMP 20x certification (FedRAMP Marketplace) | Yes | No |
| Full email and collaboration suite inside the compliance boundary | Yes | No |
| Cross-framework support for SOC 2, ISO 27001, HIPAA, and other standards | Yes | No |
| Award-winning GRC platform | Yes | No |
PreVeil information is based on PreVeil's public materials, including its CMMC compliance and NIST 800-171 pages, its VDI and pricing pages, and its VDI service addendum. FedRAMP Marketplace and Cyber AB Marketplace listings were checked at publication.
Who PreVeil is a fit for
| PreVeil can be the right fit when | Secureframe Defense is the better fit when |
|---|---|
| Your CUI lives only in email and file attachments | CUI touches endpoints, CAD models, procurement portals, or engineering tools |
| You want to keep your commercial Microsoft 365 or Google Workspace tenant with no migration | You need the full collaboration suite (calendar, Teams or Meet, SharePoint or Drive, Office apps) inside the compliance boundary |
| A documentation package plus templates fits how you run compliance | You want your SSP, evidence, and SPRS score generated from your live environment |
| A 3-seat entry point works: PreVeil Pass is $450 per month for 3 Gov Community licenses, prepaid for 12 months | You also carry SOC 2, ISO 27001, or HIPAA obligations and want one evidence library |
PreVeil publishes no 1- or 2-seat CMMC price, so even a 1 or 2 person shop starts from the 3-seat PreVeil Pass package or a custom quote. Richard Wakeman, Chief Security Architect for Microsoft's U.S. Aerospace and Defense vertical, says about 90% of the customers he works with go into GCC High versus 10% into GCC, because they hold or expect export-controlled data. GCC High and Google Workspace are built and secured by Microsoft's and Google's engineering organizations, with the full office suite, admin controls, and scale that come with them.
Planning your program? Start with our CMMC compliance hub, download the CMMC Level 2 compliance checklist, or see how Secureframe Defense compares to Summit 7.
Complete CMMC coverage
Secureframe Defense covers the full set of NIST 800-171 controls. Defense Navigator scopes your environment and maps every applicable requirement, then the platform provisions compliant infrastructure, enforces configurations, collects evidence, and tracks every control in one place. You see exactly what’s covered, what’s in progress, and what’s left.
PreVeil states its platform supports 102 of the 110 controls and hands you templates for the rest. Implementing them, collecting evidence, and keeping them current falls to your team, spread across separate tools for endpoint security, audit logging, vulnerability management, and training.
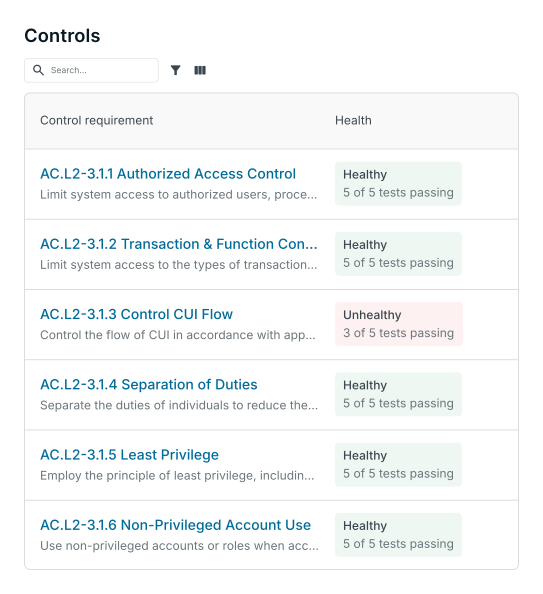
Built to protect CUI wherever it lives
Email and file sharing are common CUI channels, but they’re rarely the only ones. Technical drawings arrive through procurement portals. CUI lands on laptops, in project management tools, and in manufacturing systems.
Secureframe Defense secures CUI at the environment level: a compliant enclave with Windows 11 virtual desktops (2 vCPU and 8 GB up to 8 vCPU and 32 GB, plus a GPU tier) or Federal MDM controlling access, so CUI stays protected however it flows through your business.
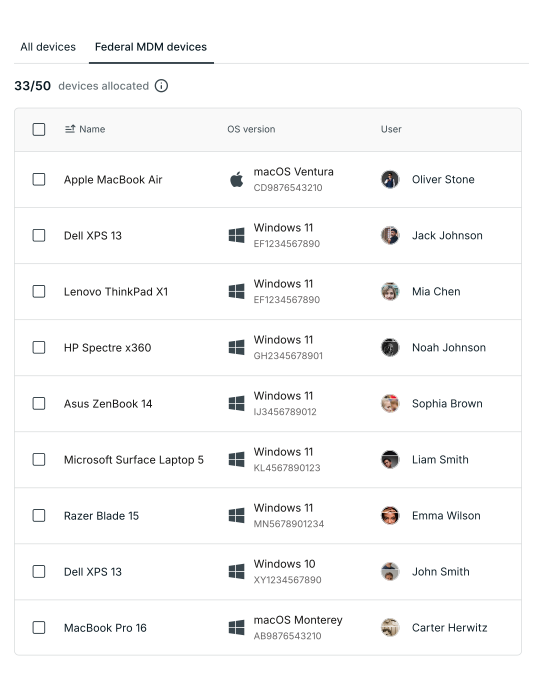
One platform instead of a stack of tools
Every additional tool in a compliance program adds cost, integration work, and another place evidence can fall through the cracks. A self-assessment evaluates your whole environment, and gaps between tools are where findings live.
Secureframe Defense consolidates the enclave, endpoint management, documentation, monitoring, training, and vendor risk into one platform with one evidence library. When your SPRS score is calculated it reflects your full environment, not a patchwork of exports from separate systems.
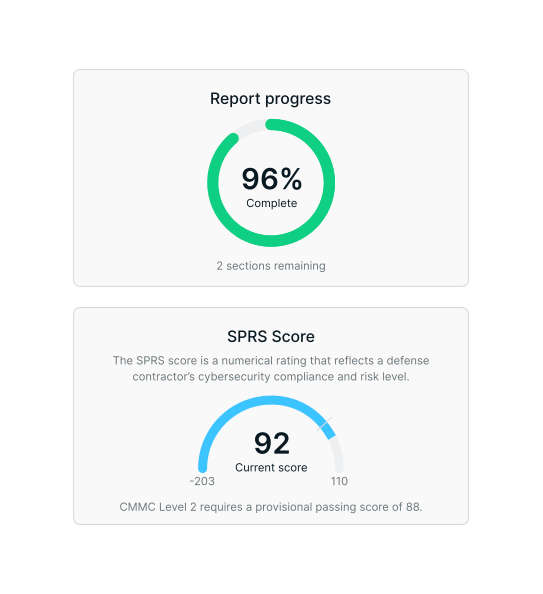
Documentation generated from your live environment
An SSP is only useful if it reflects your real environment. Secureframe Defense generates implementation statements for all 320 assessment objectives from your connected tech stack, keeps them current as configurations change, and maintains a live SPRS score your senior official can stand behind at annual affirmation.
With an overlay approach, documentation only covers what the overlay sees. The rest of your environment, including the endpoints, logging, and systems outside the encrypted boundary, still needs to be documented, evidenced, and kept current.
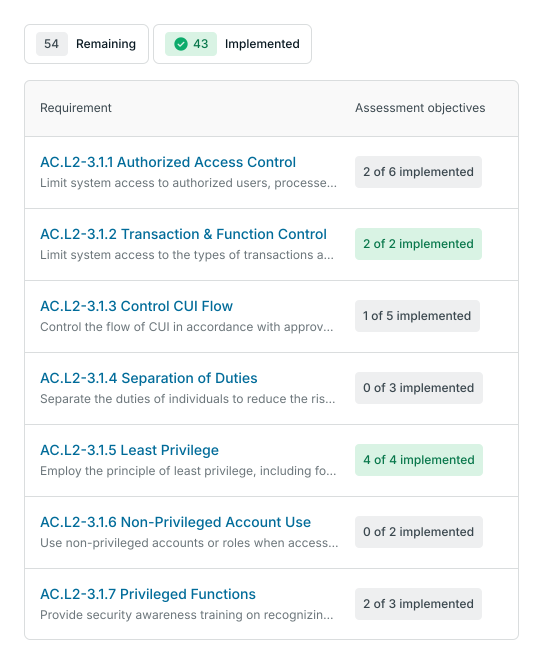
“Secureframe was easy to use
It’s clearly purpose-built for the DIB community and the CMMC program. Our assessment team absolutely loved working with the platform for Secureframe’s own Level 2 assessment.”
Robert Teague
VP of Federal Consulting, Redspin
“It’s the peace of mind that Secureframe provides.
The continuous monitoring, the fact that we have a system as opposed to a person trying to manage all of this. That’s the value add for us.”
Stephanie Castro
Director of Operations, Adyton
“Secureframe has saved us at least 500 hours.
Going into each platform to demonstrate how each of 320 control objectives is implemented, continuously, is a massive lift.”
David Hoenisch
Lead Cybersecurity Engineer, Manufacturing Consulting Concepts
We're a leader in federal compliance automation and cybersecurity
Navigate the complexity of contractual CMMC cybersecurity requirements with a team of federal experts dedicated to your success and national security.

CMMC Level 2 Certified
We were in the first 0.5% of the ~80K expected Level 2 organizations that got certified in September 2025.
FedRAMP 20x Class C (Moderate) Certified
The Secureframe Platform is FedRAMP Certified at Class C (Moderate) through the 20x program, audited by Coalfire Federal, after being among the first 20x authorizations in August 2025.

25+ CMMC Registered Practitioners
We’re a CMMC Registered Practitioner Organization listed in the CyberAB Marketplace since March 2025.

See what automated CMMC compliance looks like
Book a demo
FAQs
According to PreVeil’s own materials, its platform supports 102 of the 110 NIST 800-171 controls and provides pre-filled documentation for all 110. Implementing the remaining controls, collecting evidence, and keeping them current falls to your team. Secureframe Defense covers the full control set with guided scoping and evidence generated from your live environment.
Yes. PreVeil announced on July 6, 2026 that its managed service offering, covering PreVeil VDI and Email Relay, passed a CMMC Level 2 assessment with a 110 out of 110 score. Secureframe earned its own CMMC Level 2 certification in September 2025 after a C3PAO assessment by Redspin, and is a Registered Provider Organization in the Cyber AB Marketplace.
Yes. PreVeil is an overlay that encrypts email and file sharing inside your existing environment. The endpoints, logging, and systems that touch CUI still need compliant configuration, documentation, and evidence. Secureframe Defense provides that compliant environment, with your choice of Microsoft GCC High or Google Workspace Enterprise Plus with the Assured Controls Plus add-on, configured automatically and continuously monitored for drift.
No. PreVeil deploys alongside your existing Microsoft 365, Exchange, or Google Workspace tenant, so you keep paying for that underlying subscription. It sells encrypted email and file sharing (PreVeil Email and Drive) plus a documentation package; as of August 2026 it offers no calendar, contacts directory, chat, meetings, or document co-authoring. Those stay on the commercial tenant you already run, with CUI scoped to PreVeil’s email and Drive.
No. PreVeil does not appear on the FedRAMP Marketplace under any status; see PreVeil’s site for its own description of its FedRAMP posture. The Secureframe Platform is listed on the FedRAMP Marketplace as FedRAMP Certified, 20x, Class C (Moderate), audited by Coalfire Federal.
As of August 2026, PreVeil’s published pricing is: Basic, free with 5 GB; Individual, $25 per month billed annually; Business, $30 per user per month with a 24-month minimum for 3 to 9 users; and Gov Community, its CMMC, DFARS 7012, and ITAR tier, custom quoted. PreVeil Pass, its smallest published CMMC package, is $450 per month for 3 Gov Community licenses on a 12-month prepaid contract. No 1- or 2-seat CMMC price is published.
Yes, since mid-2026. PreVeil VDI runs on Amazon WorkSpaces in AWS GovCloud with Okta and ThreatLocker preconfigured. PreVeil publishes no Windows version, machine sizes, GPU option, or price, and its guides require the AWS WorkSpaces desktop client. Secureframe Virtual Desktops run Windows 11 in Azure Government with documented sizes from 2 vCPU and 8 GB to 8 vCPU and 32 GB plus a GPU tier, deployed into an Azure subscription you own.
No. PreVeil sells no MDM product; its endpoint guidance points to third-party tools such as Microsoft Intune, and the endpoint control it ships is ThreatLocker allowlisting inside its VDI. Secureframe Defense offers Federal MDM for Windows, macOS, and Linux, a FedRAMP Moderate authorized option managed by Secureframe, at $15 per device per month.
As of July 1, 2026, GCC High lists at $35.80 (Business Premium) to $97.50 (G5) per user per month through resellers. PreVeil’s CMMC tier, Gov Community, is custom quoted; its smallest published CMMC package, PreVeil Pass, is $450 per month for 3 seats, and you still pay for the commercial email plan underneath the overlay. PreVeil’s savings figures versus GCC High are its own total-cost claims, driven by licensing only CUI users and avoiding migration. Compare total cost for your seat mix, migration, and tooling.
PreVeil is an encrypted overlay on your existing Google Workspace tenant; it does not configure the tenant. Google’s route to CMMC Level 2 is Workspace Enterprise Plus with the Assured Controls Plus add-on, priced by quote. Secureframe Defense configures that setup automatically and continuously monitors it, or stands up Microsoft GCC High instead, so CUI lives in a fully compliant suite rather than only in encrypted email and files.
Yes. Contractors sometimes keep PreVeil for encrypted communication while using Secureframe Defense for the enclave, endpoint management, documentation, monitoring, and the rest of the control set. Secureframe connects to your environment, scopes the applicable requirements, and generates your SSP, POA&M, and evidence from one platform covering your full environment, including the systems an email and file-sharing overlay does not see.